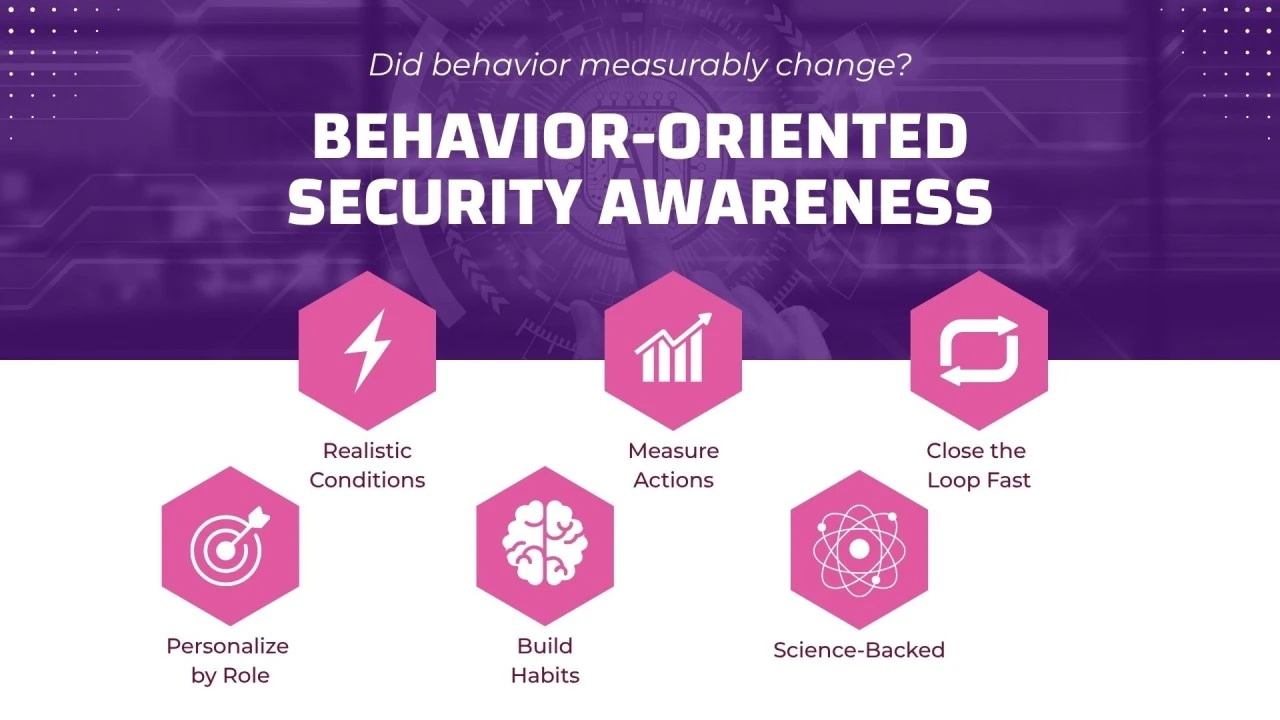
Behavior-oriented awareness means the primary success metric is observable risk behavior change, not knowledge completion, positive feedback scores, or course consumption.
1. Focus on decisions under realistic conditions
Humans do not fail because they lack information.
They fail because of:
- Time pressure
- Cognitive overload
- Authority bias
- Urgency framing
- Habit shortcuts
Behavior-oriented awareness trains decision-making under these conditions – not in a calm e-learning environment.
2. Measure actions, not attitudes
Traditional metrics:
- Course completion rate
- Quiz score
- Satisfaction score
- Reduced phishing click rate (often artificially easy simulations)
Behavior-oriented metrics:
- Reporting speed
- Escalation quality
- Secure handling of real suspicious events
- Reduction in risky patterns over repeated simulations
- Transfer effects across attack types
If behavior does not measurably shift, the program is ineffective – regardless of engagement.
3. Close the loop immediately
Behavior change requires:
- Immediate consequence
- Immediate micro-learning
- Repetition
- Reinforcement in context
Example: A user clicks → instant feedback means learning impulse → short contextual explanation → similar but slightly varied simulation later → behavioral reinforcement.
Not: click → quarterly training reminder.
4. Personalization
Behavior change is strongest when:
- The scenario matches the user’s role
- The attack reflects realistic threat exposure
- The difficulty adapts over time
- Individual risk patterns are addressed
Generic training cannot target behavioral weaknesses.
5. Habit formation, not awareness
The end goal is automatic behavior:
- Hover before click
- Verify sender
- Report instinctively
- Slow down when urgency appears
When secure behavior becomes reflexive, awareness has succeeded.
6. Scientific foundation
Behavior-oriented awareness draws from:
- Behavioral psychology
- Stress decision theory
- Habit loop research
- Exposure training
- Adaptive learning systems
It treats employees as human decision systems – not as information storage units.
In short:
- Behavior-oriented awareness does not ask “Did they understand?”
- It asks “Did their real-world behavior measurably change?”