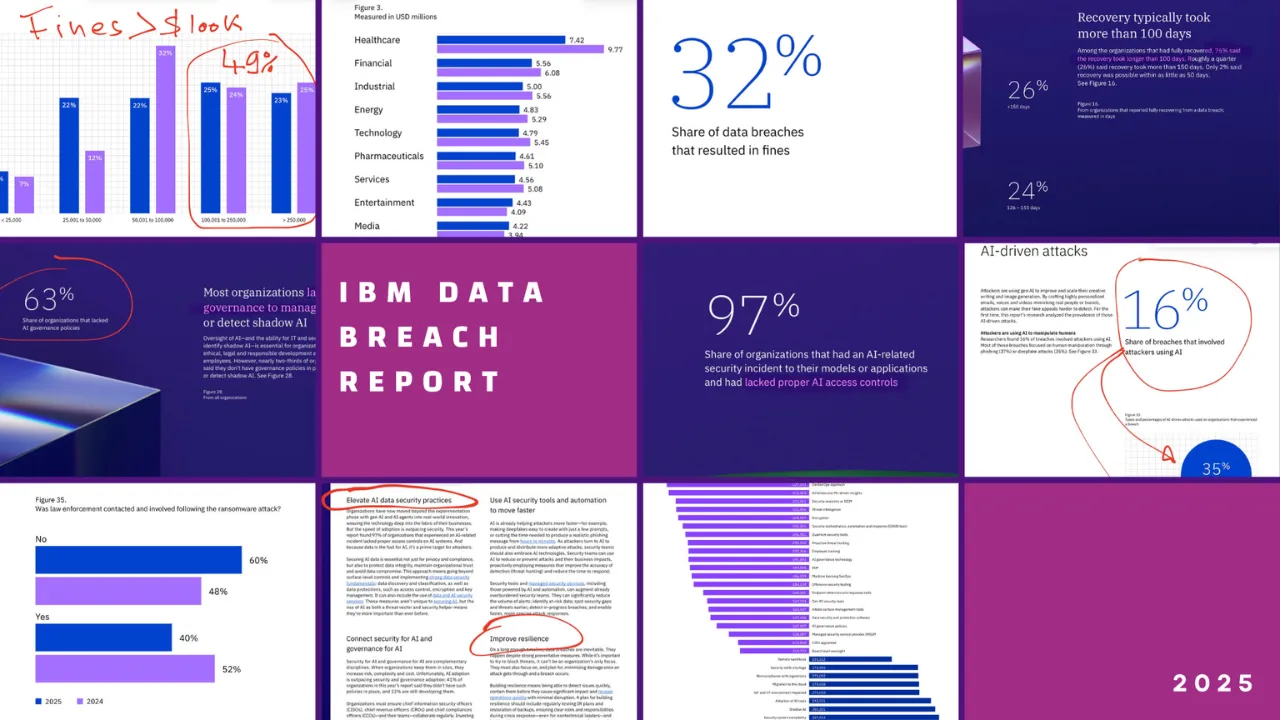
IBM’s Cost of a Data Breach Report 2026 puts the global average at a record USD 4.99 million. But the headline number tells you less than two others buried in the same report: 63% and 247.
A record USD 4.99 million, and what drove it
A data breach has never been cheap. But in 2026, the numbers moved in the wrong direction again.
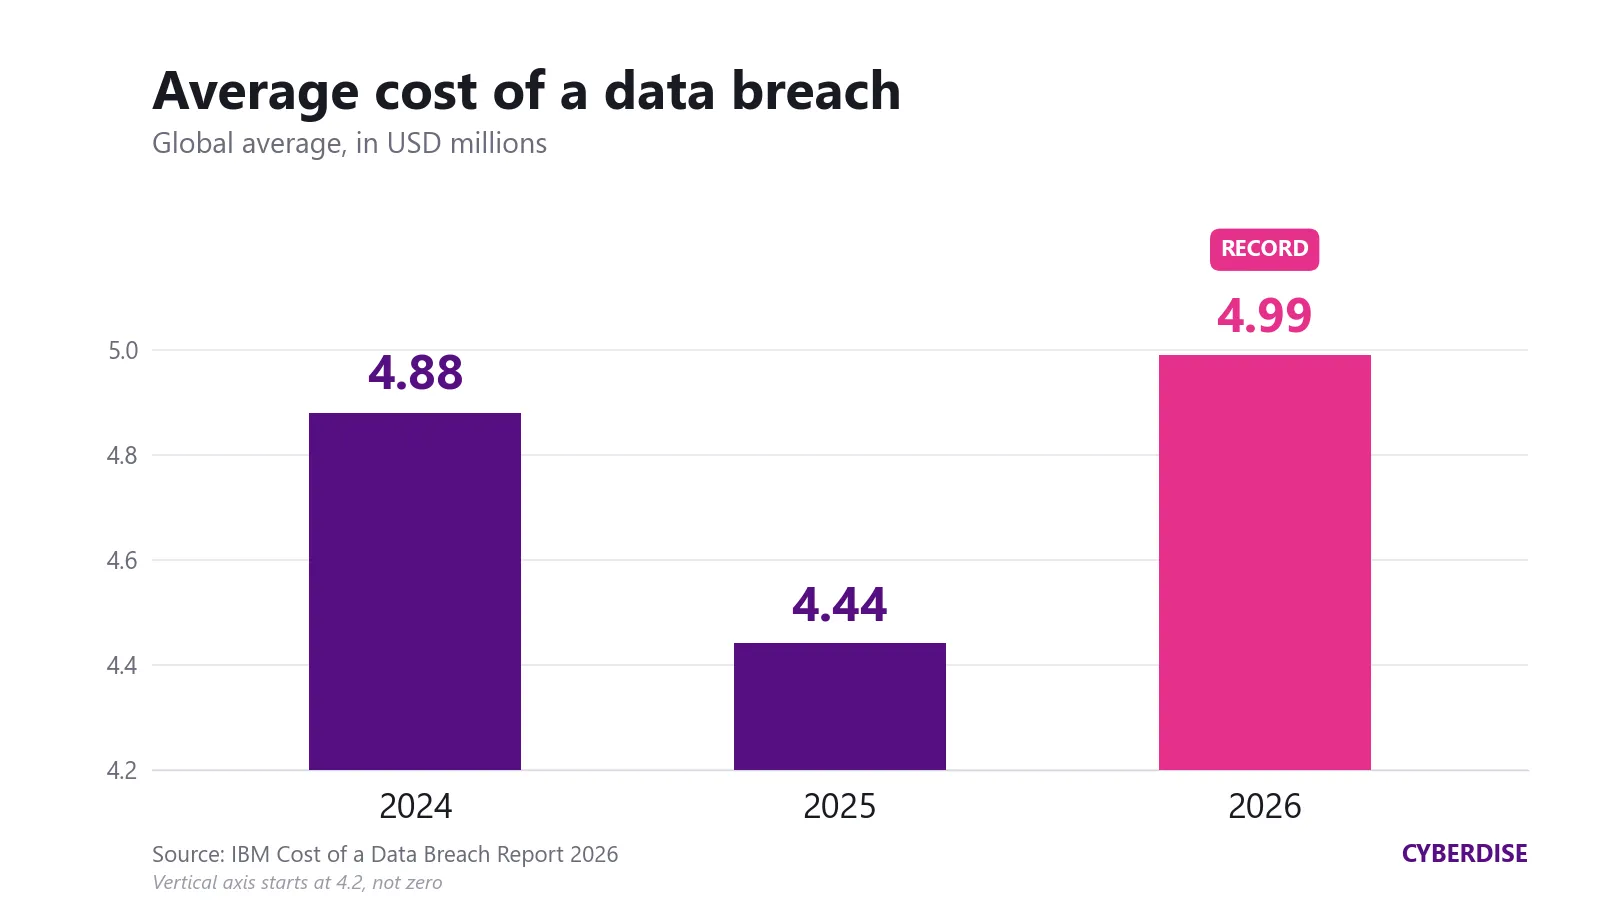
According to IBM’s Cost of a Data Breach Report 2026, the global average cost of a breach reached a record USD 4.99 million — up 12% from USD 4.44 million in 2025. Much of that increase came from detection and escalation costs and from lost business after the incident.
Two details make that increase sharper than it first looks. The 12% is not a smooth climb: 2025 had actually fallen to USD 4.44 million from USD 4.88 million the year before. So this is a rebound and a record at once — the highest figure in the eight years IBM has tracked.
And the split is precise. Detection and escalation plus lost business drove 63% of this year’s record, together accounting for USD 3.18 million of the USD 4.99 million total. Each rose 11.5%. The category that grew fastest, though, was post-breach response — regulatory fines, legal costs, credit monitoring — up 15%. If you have been treating NIS2 as a documentation exercise, that line is worth a second look.
The global average hides enormous differences
In the United States, an average breach now costs USD 11.5 million — more than twice the global average. Germany, meanwhile, saw one of the larger increases in Europe: costs rose 18% to USD 4.93 million.
Industry matters just as much. Healthcare remains the most expensive sector at USD 6.64 million per breach, followed closely by financial services at USD 6.29 million. At the lower end of IBM’s industry comparison, the public sector still averaged USD 3.5 million.
So what does the USD 4.99 million headline really tell us?
Probably less about what your next breach will cost — and more about the direction of travel.
Breach costs are rising again. Geography, regulation, industry, the type of data involved and, above all, how quickly an organisation detects and contains an attack can move the final number dramatically. Marks & Spencer’s £300 million is what the far end of that range looks like in practice.
The number that should worry you isn’t 4.99
It’s 247.
That is the mean number of days organisations needed to identify and contain a breach — 183 days to spot it, another 64 to shut it down. Eight months from break-in to containment. And after five straight years of improvement, that clock went the wrong way this year, up 2.5%.
The cost of the delay is measurable. Breaches running longer than 200 days averaged USD 5.65 million. Those resolved faster averaged USD 4.32 million. A gap of USD 1.33 million — decided not by the sophistication of the attack, but by how long nobody noticed.
Which is really the same point as the 63%: most of what a breach costs is not the break-in. It is everything that happens while the intruder is still inside. That is also why awareness has to become continuous rather than annual — the people closest to an attack are usually the first ones able to raise a hand.
More than one in four organisations were hit by an AI-driven attack
The other shift in this year’s report is who is doing the attacking.
More than a quarter of organisations experienced a malicious AI-driven attack — a 56% increase over last year. Those attacks cost USD 6.04 million on average, against USD 5.03 million for malicious attacks without AI. A million-dollar premium for automation.
Deepfake impersonation was the single largest category at 45% of AI attacks. Generative AI makes social engineering cheap to produce and hard to detect, which is exactly why it is being pointed at people rather than firewalls — and why voice-clone calls stopped being a novelty this year.
Two numbers underneath that are worth sitting with. Security incidents involving shadow AI — staff using unapproved AI tools — more than doubled to 43%, from 20% last year, and cost more when they happened: USD 5.39 million against USD 4.63 million. And ransomware turned up in 39% of breaches, continuing a four-year climb from 24% in 2023.
And with AI-driven attacks increasing the speed and scale of cyberattacks, that last factor may become increasingly important.
The real question for security leaders is therefore not whether a breach costs $4 million, $5 million or $10 million. It is how much of that cost can still be prevented by detecting and containing the attack faster. And: some regulator will punish you anyway…
So Long, Palo
Source
All figures: IBM Cost of a Data Breach Report 2026. Figures 1–5, 17, 21–22 and 30.