What every security leader should understand before funding another awareness campaign. This is an essay about engineering human defences — why annual training can’t keep pace with AI-driven attacks, what continuous security awareness actually requires, and how everyday users and the IT security team can work far more closely together.
The largest attack vector is now people
In my previous article, I argued that most “cyber attack” infographics classify threats badly. They mix malware, vulnerabilities, attack techniques and threat actors into one colourful diagram that looks convincing and explains very little. My fix was simple: stop classifying attacks by technical label, and classify them by their primary attack vector instead.
Do that, and one thing stands out immediately. The largest — and fastest-growing — category is no longer malware.
It’s people. More precisely: social engineering and attacks on human behaviour.
If you accept that, it has consequences. Because if the primary attack vector has changed, shouldn’t our defensive strategy change with it? I think it should.
Built for yesterday: how AI changed the economics of cybercrime
Traditional security awareness was built for a very different world. Attackers sent phishing emails full of spelling mistakes. The fake landing pages looked terrible. Most attacks relied on volume rather than quality.
So the logical response was education: teach employees to spot suspicious emails, explain the common warning signs, run the occasional phishing simulation, repeat the training once a year.
For a long time that was perfectly reasonable. But the world moved.
AI didn’t invent phishing, malware or social engineering. What it changed is more fundamental than any technique.
Economics.
For the first time, attackers can produce genuinely convincing attacks at almost no cost. They can harvest public information from LinkedIn and everywhere else, analyse company websites, imitate a specific writing style, translate flawlessly into nearly any language, clone a voice, even generate convincing video.
And they can do it thousands of times a day.
What used to require an experienced attacker now requires little more than a prompt. The barrier to entry has collapsed.
Knowledge isn't enough when attacks target behaviour
This is where I think many awareness programmes quietly break. They rest on a simple assumption:
Knowledge → Secure Behaviour
If employees know what phishing looks like, they will decide better. It sounds reasonable. Human psychology just doesn’t work that way.
I know eating less sugar is good for me. I still eat too much of it. I know I should work out more. I don’t. I know I shouldn’t look at my phone while driving — and sometimes I still do. I doubt I’m the only one.
Knowledge influences behaviour. It rarely determines it. Cybersecurity is no exception — we’ve written before about why attitude and behaviour are not the same thing, and why so many programmes end up training the wrong thing.
AI-powered attacks rarely exploit a gap in technical knowledge. They exploit predictable human behaviour: trust, authority, curiosity, urgency, fear, routine, time pressure. If you want the mechanics, we’ve unpacked the psychology behind why people click in detail.
The attacker doesn’t need you to misunderstand technology. The attacker needs you to behave like a normal human being. And under pressure, normal human behaviour is remarkably predictable — which is exactly what modern attackers are counting on.
Behaviour is learned through practice
There are professions where a mistake costs lives. Pilots don’t learn emergency procedures from slides. Firefighters don’t prepare for a disaster by watching a video once a year. Surgeons don’t become proficient by passing an online quiz.
They drill. Again and again, until the correct action becomes muscle memory.
Cybersecurity should work the same way. Under stress, nobody recalls a training session from six months ago — people fall back on habit. That’s precisely what happened to me when I got phished this spring.
What our research with HSLU found
With researchers at the Lucerne University of Applied Sciences (HSLU), we set out to answer one deliberately simple question: what actually changes defensive behaviour? Knowledge, delivered as training? Or practice, delivered as drills — and if so, which kind?
We compared three approaches [1]:
- Traditional awareness eLearning — improved defensive behaviour by roughly 40%.
- Conventional phishing simulations — slightly better than eLearning.
- AI-personalised spear-phishing simulations using OSINT data — improvements of up to 60%.
The conclusion is not that training is useless. Knowledge remains essential: people have to know, and most organisations also have to demonstrate that employees are compliant with a policy, a law or a certification.
But knowledge on its own doesn’t get you there. Behaviour changes most when people repeatedly make decisions under realistic conditions. So let’s engineer the behaviour we actually want. 🙂
From campaigns to continuous security awareness
Too many programmes still run as isolated campaigns. An employee completes a course. They get a phishing simulation, or a set of standard exercises — often the kind we’ve argued are mostly pointless as they’re run today. A score is recorded. The campaign closes. Sometimes there’s a certificate.
Attackers don’t work in campaigns.
They adapt continuously — and so does their AI. They learn, experiment, change tactics, exploit current events, and move across channels: email to SMS, SMS to voice, voice to collaboration platforms, and on to deepfakes. At machine speed.
Our defences should move at a comparable speed. And employees shouldn’t just be trained for this reality — they should actively contribute to defending the company.
“How do we train employees?” is, to me, yesterday’s question. The better one is:
“How do we continuously improve defensive behaviour?”
That’s a fundamentally different question, because it shifts the focus from education to engineering. From annual campaigns to continuous adaptation. It stops depending on static training and exercise libraries, and starts using real threats as immediate exercises that immunise the workforce.
It also changes what you measure. You stop tracking course completion as the headline number and start measuring the right thing — actual behaviour. You favour real-time intervention over static content.
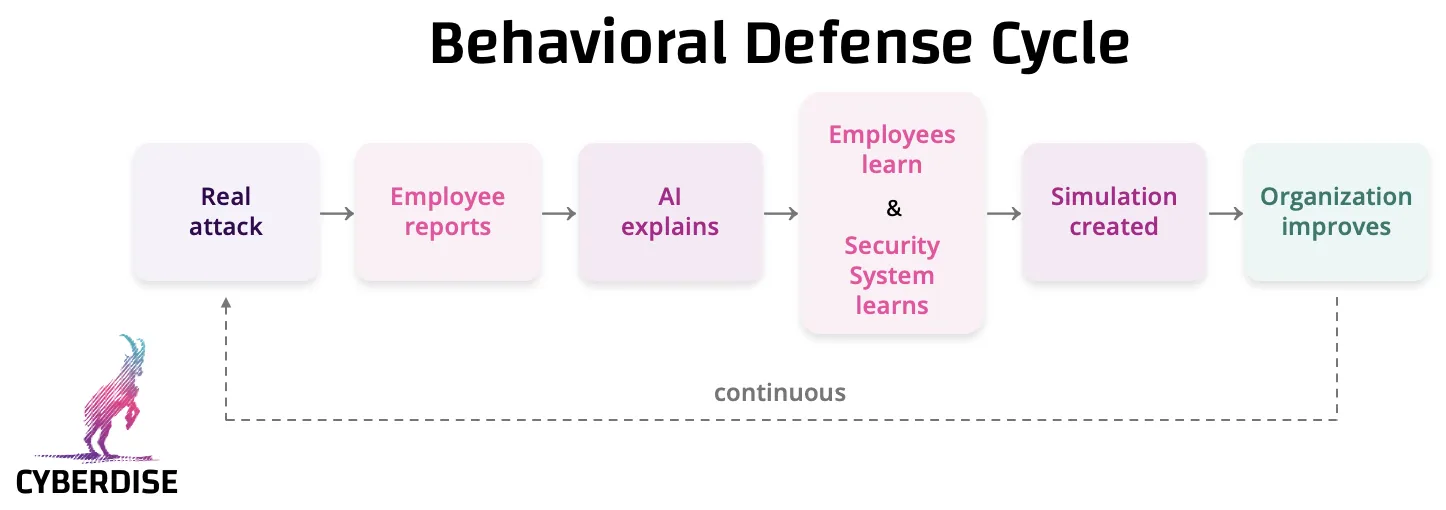
In practice, the loop looks like this. A real attack arrives. An employee reports it. AI explains what it was and why it worked. The employee learns — and so does the security system. That real attack then becomes a simulation for everyone else. The organisation improves. And then it starts again.
Some in the industry call this continuous security awareness. I’d go one step further and call it what it really is: Behavioral Defense Engineering.
The future isn't more training
For more than twenty years, security awareness has concentrated on increasing knowledge. That made sense when attacks exploited technical ignorance and user maturity was low. Today’s attacks exploit behaviour instead — so a different mindset is needed.
Not because awareness has become obsolete. Because awareness alone is no longer sufficient. Knowledge still matters; deliberate practice becomes essential; continuous adaptation becomes mandatory. And measuring real behaviour becomes considerably more valuable than counting completed courses.
The organisations that see this shift won’t necessarily run more training than everyone else. They’ll build a stack that:
- continuously strengthens human behaviour as attackers continuously evolve their own, and
- treats well-trained user behaviour as an active part of the security stack — turning human signals into high-quality, very early attack intelligence.
Because in the age of AI, cybersecurity isn’t only about protecting technology. It’s about engineering the behavioural defences of the people who use it. The state worth aiming for is the one where every attack becomes an opportunity to strengthen the organisation.
I don’t believe the future of cybersecurity belongs to whoever delivers the most awareness training. I believe it belongs to organisations that can continuously observe, strengthen and adapt human defensive behaviour as fast as attackers adapt their offensive techniques. If that behavioural signal feeds into security systems in real time, better still.
Taken together, that isn’t a better awareness programme.
It’s a different discipline — and I think it will define the next generation of human cyber defences.
So Long, Palo
Footnotes
[1] Improving Cyber Risk Behavior through AI-Enabled Spearphishing – A Comparative Analysis (joint study with the Lucerne University of Applied Sciences)