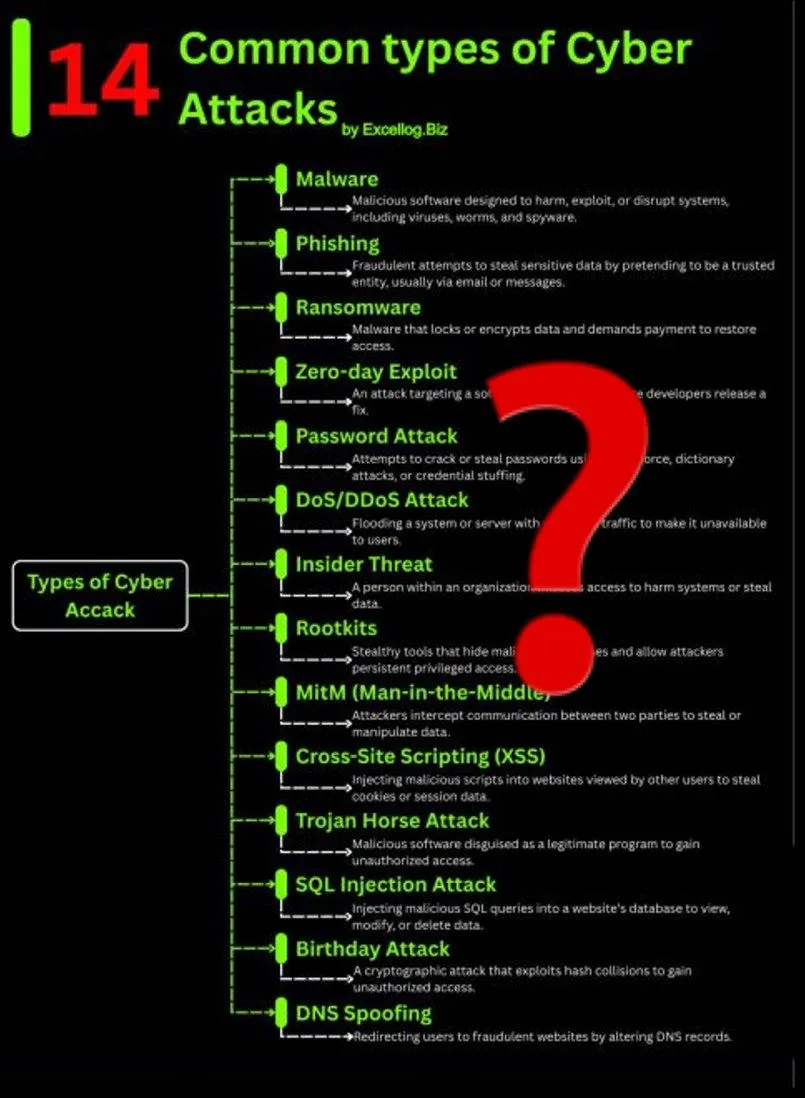
Last week I came across yet another infographic claiming to show the “14 Common Types of Cyber Attacks. [1]” At first glance, it looked convincing. Clean design, attractive colours, a professional layout. It was probably generated with AI—and that’s perfectly fine.
Unfortunately, the content wasn’t. The graphic mixed together malware families, attack techniques, vulnerabilities, threat actors and attack objectives into one seemingly logical list. It looked educational, but in reality it explained very little. That may sound like a technicality, but it isn’t.
How we classify cyber attacks fundamentally shapes how we understand them. It influences how we educate employees, where we invest our security budgets and how we build our defensive controls. A poor taxonomy leads to poor decisions — so here is a clearer cyber attack taxonomy for 2026.
What’s wrong with most cyber attack infographics
Most “Top 10” or “Top 20” cyber attack graphics often make the same mistakes. They mix completely different concepts into one list. Here are just a few examples:
Malware is a category. Trojan Horse and Rootkits are types of malware. Phishing is a social engineering technique. And so on.
These concepts are all valid — but they don’t belong on the same level.
One question first: the primary attack vector
For me, it’s not really relevant which attacks exist. What matters far more is one question:
“What is the attacker’s primary attack vector?”
Because that shows me what the attacker is trying to exploit first. Once you answer that question for yourself, the cyber threat landscape suddenly becomes much easier to understand. And maybe you’ll reach the same conclusion I did: that human-based attack vectors are increasingly coming under the spotlight. In short — the employee is becoming more and more THE target.
A practical cyber attack taxonomy for 2026
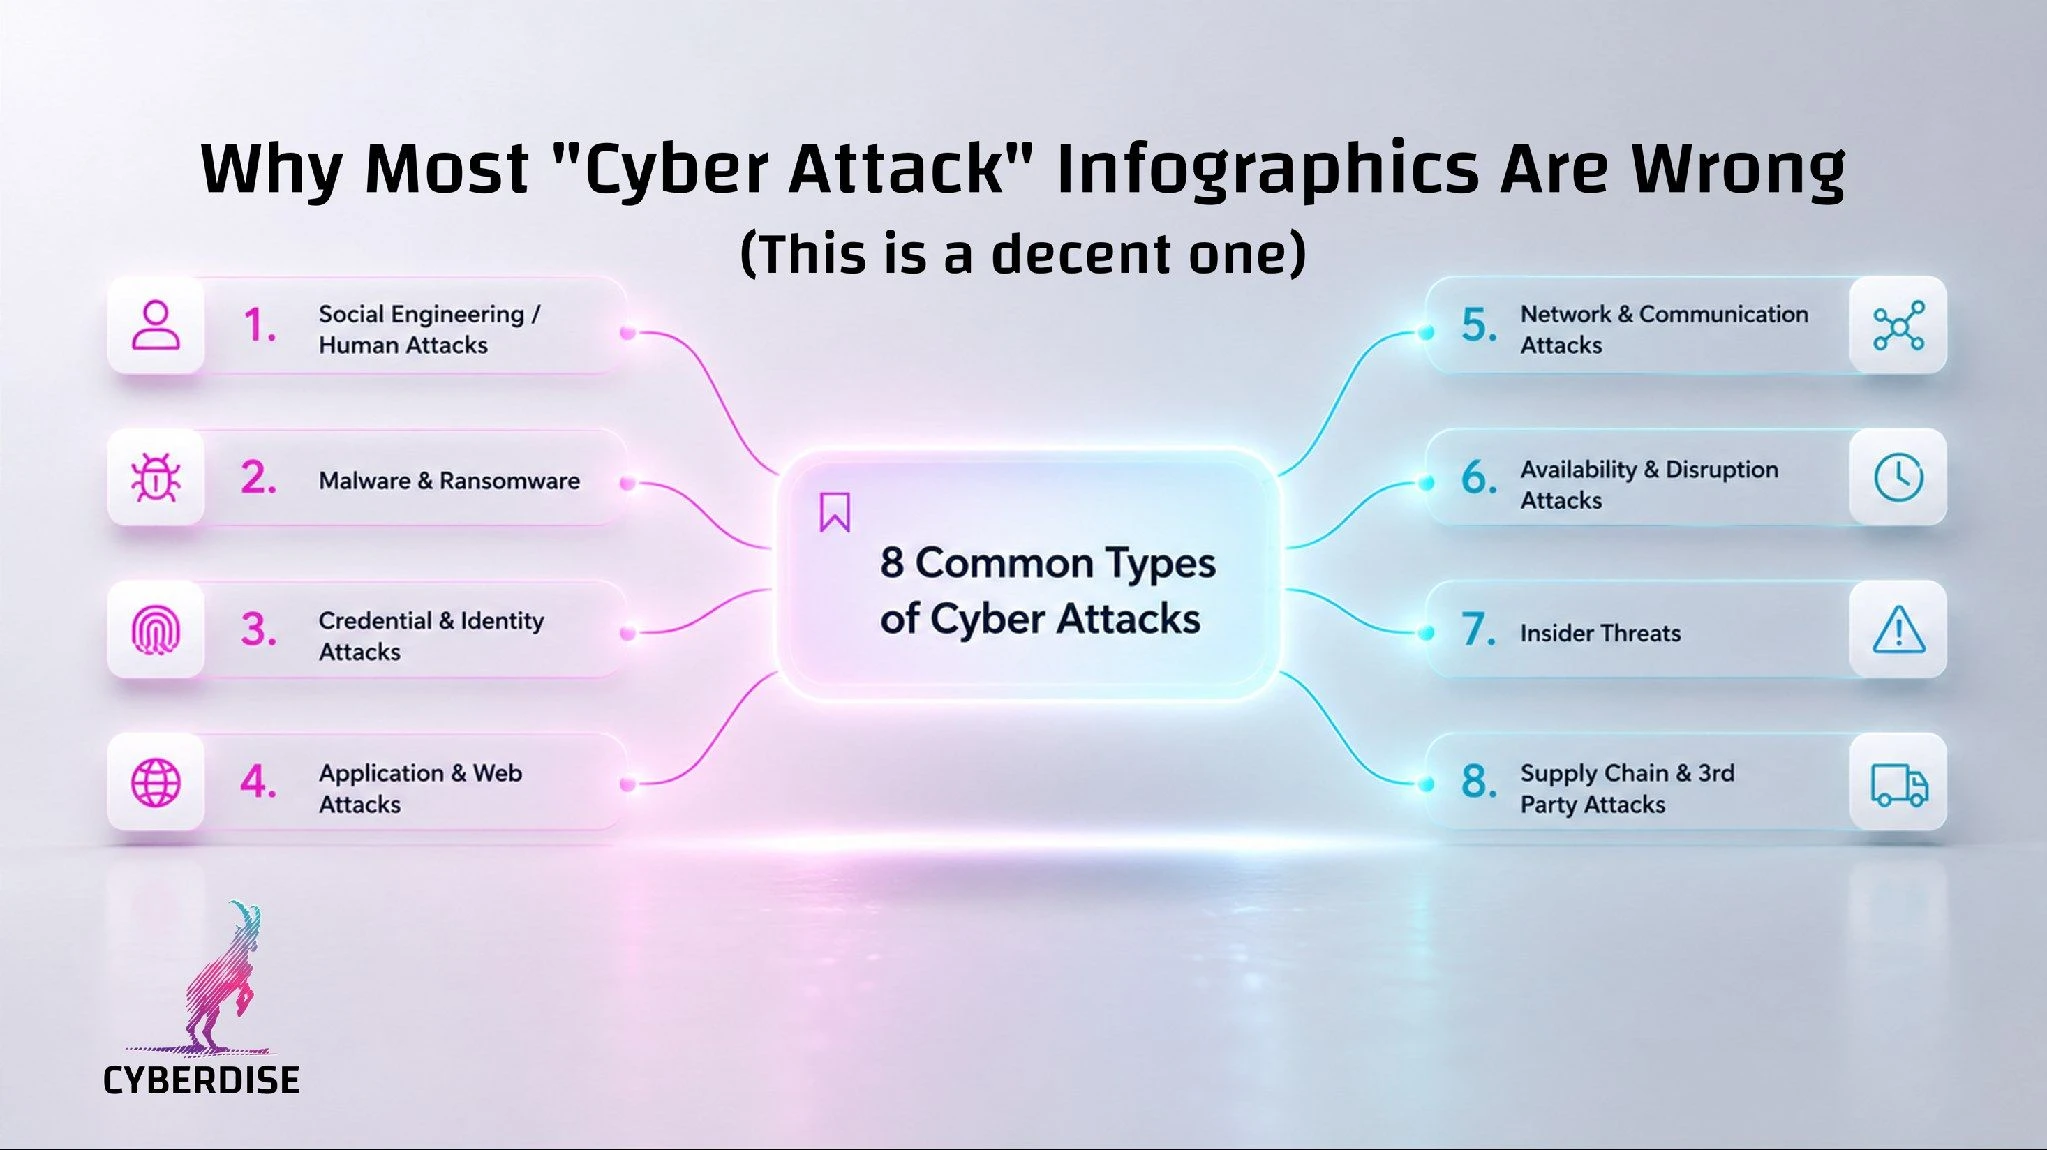
So instead of another endless list of attack names, here are eight categories — each defined by the primary attack vector the attacker exploits first.
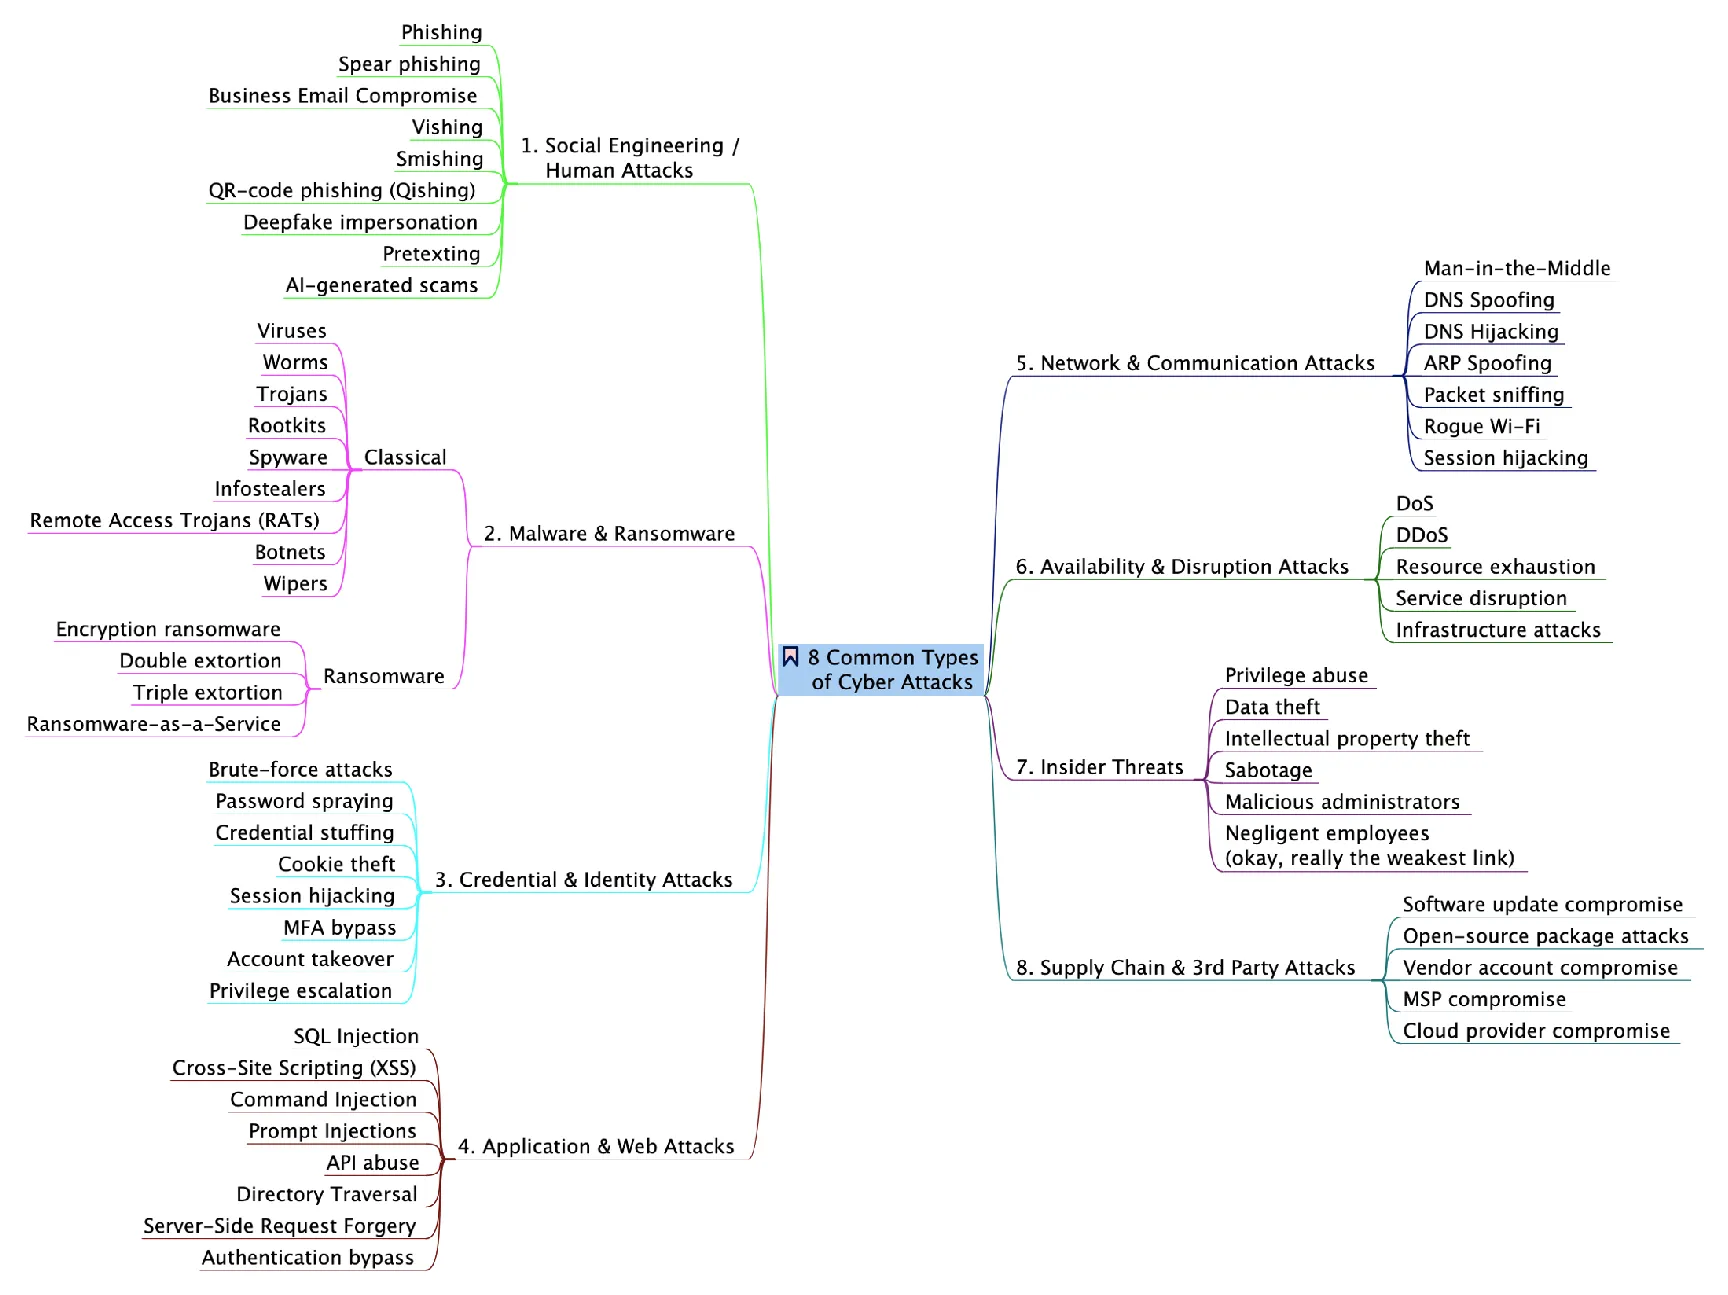
1. Social engineering / human attacks
Attack vector: People — the attacker manipulates human behaviour rather than technical vulnerabilities.
Examples include: Phishing, Spear phishing, Business Email Compromise, Vishing, Smishing, QR-code phishing, Deepfake impersonation, Pretexting, AI-generated scams.
Today, this is arguably the most important category. Modern AI lets attackers create highly personalised emails, perfect translations, cloned voices and convincing fake identities at almost zero cost. The human has become the primary attack surface.
2. Malware & ransomware
Attack vector: Endpoints and systems. Instead of manipulating people directly, the attacker deploys malicious software.
Examples include: Viruses, Worms, Trojans, Rootkits, Spyware, Adware, Infostealers, Keyloggers, Remote Access Trojans (RATs), Botnets, Wipers.
Because of its enormous business impact, ransomware deserves special attention: Encryption ransomware, Double extortion, Triple extortion, Ransomware-as-a-Service.
3. Credential & identity attacks
Attack vector: Digital identities. The goal is simple: steal or abuse valid identities.
Examples include: Brute-force attacks, Password spraying, Credential stuffing, Cookie theft, Session hijacking, MFA bypass, Account takeover, Privilege escalation.
And notice something important: phishing isn’t part of this category. Phishing is the delivery mechanism; credential theft is the objective. Those are two different things.
4. Application & web attacks
Attack vector: Software — websites, APIs and business applications.
Examples include: SQL Injection, Cross-Site Scripting (XSS), Command Injection, Prompt Injection, API abuse, Directory Traversal, Server-Side Request Forgery, Authentication bypass.
A zero-day may be involved — but it simply describes a vulnerability that was unknown or unpatched when exploited. A zero-day is not a category by itself.
5. Network & communication attacks
Attack vector: Network communications. The attacker targets protocols, routing or data transmission, exploiting technical weaknesses and especially misconfigurations.
Examples include: Man-in-the-Middle, DNS Spoofing, DNS Hijacking, ARP Spoofing, Packet sniffing, Rogue Wi-Fi, Session hijacking.
6. Availability & disruption attacks
Attack vector: Business operations. The objective isn’t necessarily to steal data — it’s to prevent systems from functioning.
Examples include: DoS, DDoS, Resource exhaustion, Service disruption, Infrastructure attacks (yes, also physical ones).
7. Insider threats
Attack vector: Trusted users — and this often hurts the most. Unlike social engineering, the attacker is already inside the organisation.
Examples include: Privilege abuse, Data theft, Intellectual property theft, Sabotage, Malicious administrators, Negligent employees.
This deserves its own category because the defensive controls are completely different.
8. Supply chain & third-party attacks
Attack vector: Trust. Rather than attacking the target organisation directly, attackers compromise a trusted supplier.
Examples include: Software update compromise, Open-source package attacks, Vendor account compromise, MSP compromise, Cloud provider compromise.
This category has become increasingly important over the past decade and is now recognised by governments and security agencies worldwide. That’s why frameworks like NIS2 and TISAX stress this attack vector. And how far along are organisations really? When we went through the latest CIO/CSO study, supply chain risk turned out to be one of the most underweighted NIS2 requirements of all — more on that in NIS2 Is in the Budget – Not Yet in the Systems.
What AI changes in 2026
Generative AI hasn’t created a completely new category of cyber attacks. Instead, AI is a big lever — it has made almost every existing category more dangerous. Attackers can now:
- generate personalised phishing emails in seconds,
- clone voices for convincing vishing attacks,
- create realistic deepfake videos,
- automate reconnaissance, analyse leaked credentials and discover software vulnerabilities faster, and
- scale attacks to millions of potential victims.
The biggest shift isn’t technical — it’s economic. Attacks that previously required skilled operators and significant resources can now be executed by almost anyone with access to AI tools. The cost of attacking has dropped dramatically, and this has been shown by current scientific studies [2], [3].
One important exception is worth mentioning. While AI hasn’t created a new category of attacks against people or traditional IT systems, it has created a new category of attacks against AI systems themselves. As organisations increasingly deploy LLMs and AI agents, attackers exploit them through techniques such as prompt injection, model poisoning, jailbreaks and training-data manipulation. In other words, AI is not only a powerful attack accelerator — it has also become a new attack surface.
The biggest change isn’t AI, it’s the attack surface
Ironically, the biggest change isn’t artificial intelligence. It’s the attack surface. For years, organisations invested heavily in protecting networks, endpoints and infrastructure — while attackers always tried to hack the human first. And it isn’t getting better: they increasingly bypass technology altogether and go after people even more.
Employees have become the shortest path into the organisation. That’s why modern cybersecurity can no longer focus solely on technical controls. It must also engineer human behaviour.
Final thoughts
Understanding cyber attacks starts with understanding attack vectors. When we mix malware families, attack techniques, vulnerabilities and threat actors into one colourful infographic, we create confusion rather than clarity. A better taxonomy improves how we think — and that’s why it matters. Because better thinking leads to better decisions, better cybersecurity and awareness programmes, and ultimately better cyber resilience.
But this raises an even more important question: if the primary attack vector has shifted from technology to people, shouldn’t our defensive strategies evolve as well?
Of course they should — and they have to! → In my next article, I’ll explain why this new way of classifying cyber attacks isn’t just academically cleaner → it fundamentally changes how organisations should approach better risk behaviour and cybersecurity awareness in the age of AI.
Because understanding the attack landscape is only the first step. Engineering human behaviour against these attacks is where the real work begins. 😉
So Long, Palo Stacho
PS: Of course, you can run all the social engineering exercises above with CYBERDISE Awareness & CYBERDISE Omnichannel…
Footnotes
[1] Weak categorisation of cyber attacks found on the web: “14 Common types of Cyber Attacks” by ExcelLog, which circulated on LinkedIn. Shown above and discussed in the opening section; reproduced for the purpose of criticism and commentary. [2] arXiv:2412.00586v1 – Evaluating Large Language Models’ Capability to Launch Fully Automated Spear Phishing Campaigns: Validated on Human Subjects. [3] Improving Cyber Risk Behavior through AI-Enabled Spearphishing – A Comparative Analysis.