CYBERDISE 3.0 contains significant new functionality in AI phishing, LMS and training, threat reporting and message analysis and even architectural enhancements. That’s why it’s a great release!
Version 3.0 since early 2026. Those who want to know what’s exactly in the release, please check out the release-notes. But here I’d like to cover the three to four features we love most 💖.
Here we go:
- Prepare your own super-realistic AI-Enabled Phishing Exercise Templates in Every Language
- The Phish-Button AND Instant Feedback
- Each user has their own personal training portal
- Multi AD on Realm Level or The Beauty of a Smart Application Architecture
- HLS-Streaming and Button Languages as 2 lovely nerdy features
Super-realistic AI phishing exercises in every language
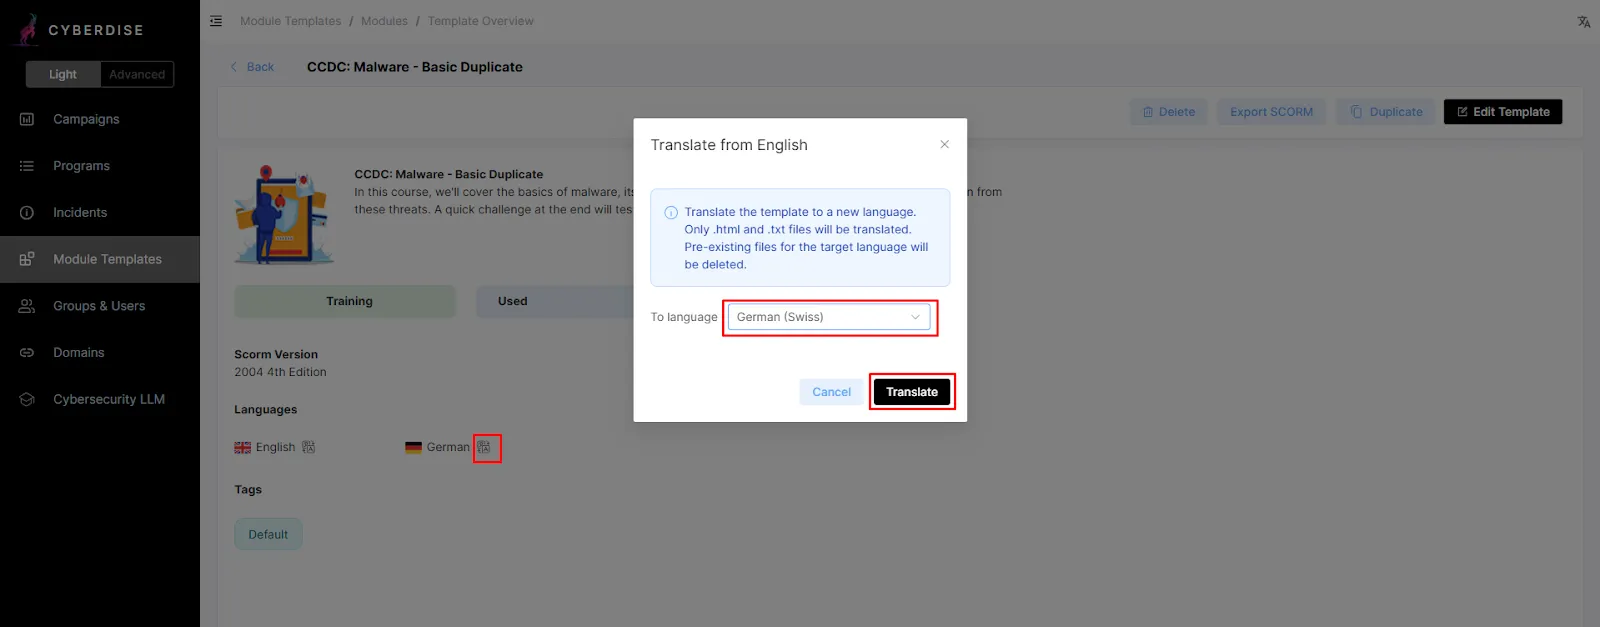
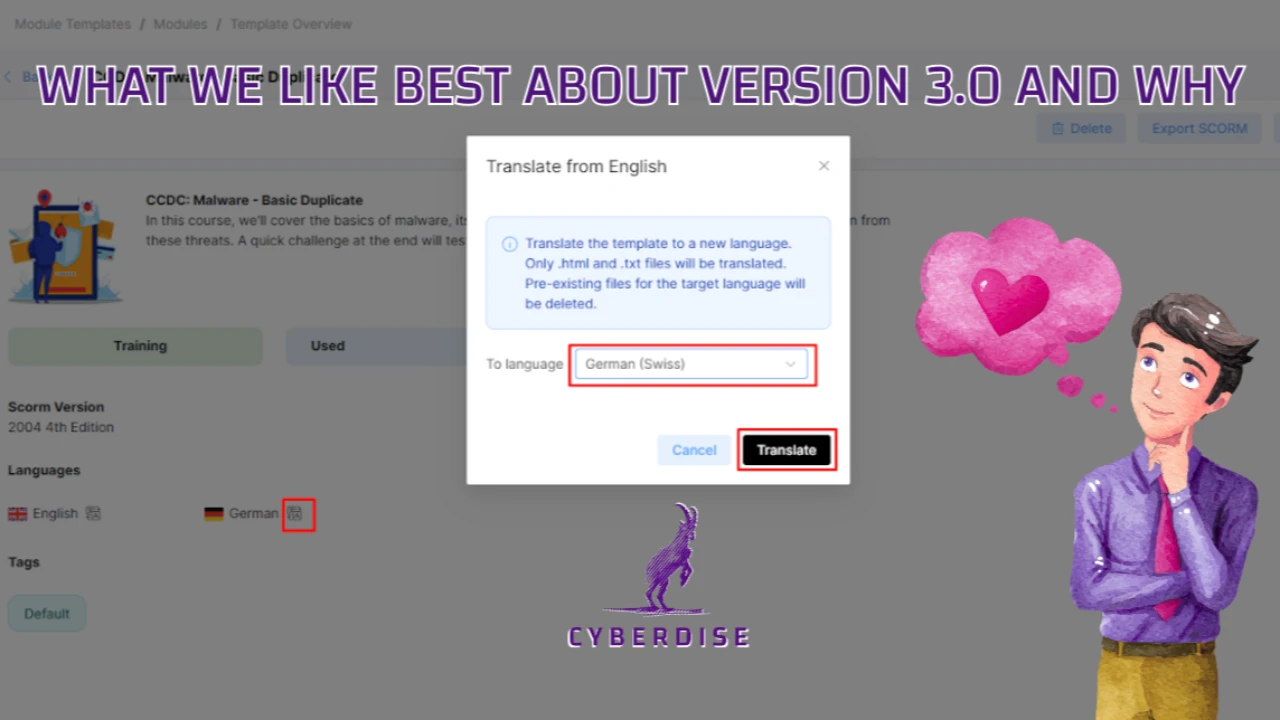
Criminals are massively using AI for preparing their own attacks. The days when you could recognize a dangerous email by its poor language or because of tpyos 😉 are gone. Today, it is also no longer sufficient to select a standard phishing template from a library for an exercise. You have to fight fire with fire; our staff must be specifically trained with AI phishing exercises. But when you are forced to use a particular AI scenario in multiple languages and countries, then this kind of work gets complicated. And this is exactly what we counter with the AI-enabled Template Translator feature. It allows you to prepare and translate your custom multilingual template or phishing simulation campaign just with a few clicks. This is a great deal for corporates and MSSP partners who are providing (AI-enabled) custom attack simulations in several languages. I love this feature!
The Phish-Button together with instant feedback
What is the goal of cybersecurity awareness? The goal is not (only) to reduce data entry or click rates. The real goal of awareness is ultimately to improve people’s risk behavior and thereby reduce security incidents. Engagement is a powerful tool for this. With engagement, our employees remain committed, and only then can we talk about “human firewalls.” And this is exactly where the button comes in. When an employee can use the button to report suspicious emails and the system responds to the report, a dialogue is created. Our instant feedback not only gives the user security, but also promotes dialogue and thus engagement.
AI assists in analyzing suspicious messages, and the resulting risk score triggers standardized responses that are sent back to the reporter. The use of configurable messages instead of a direct response from the LLM is intentional and is a frequently mentioned customer requirement.
It is clear that the phishing incident plugin (button) in combination with automatic reporting feedback increases employee engagement, automation leads to less work and faster intervention by the security team, and the risk reduction achieved becomes measurable. Great, isn’t it?
Each user has their own personal training portal
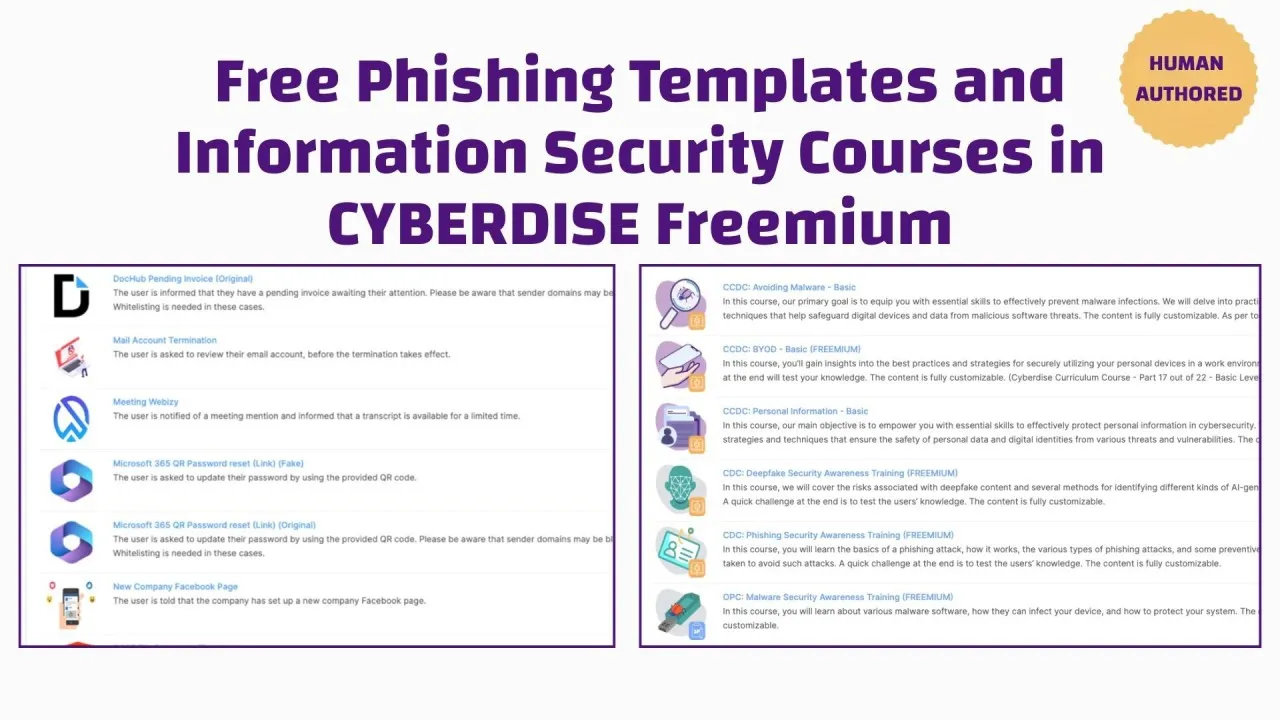
Other products often send training courses (SAT) in an email. With version 3.0 of our LMS, this is no longer necessary. Users can access the training courses provided for them in their individual training portal. And: Our import/export functions for learning content and our training reminders are also cool! You no longer need complicated and expensive LMSs; simply add your third-party content to CYBERDISE LMS.
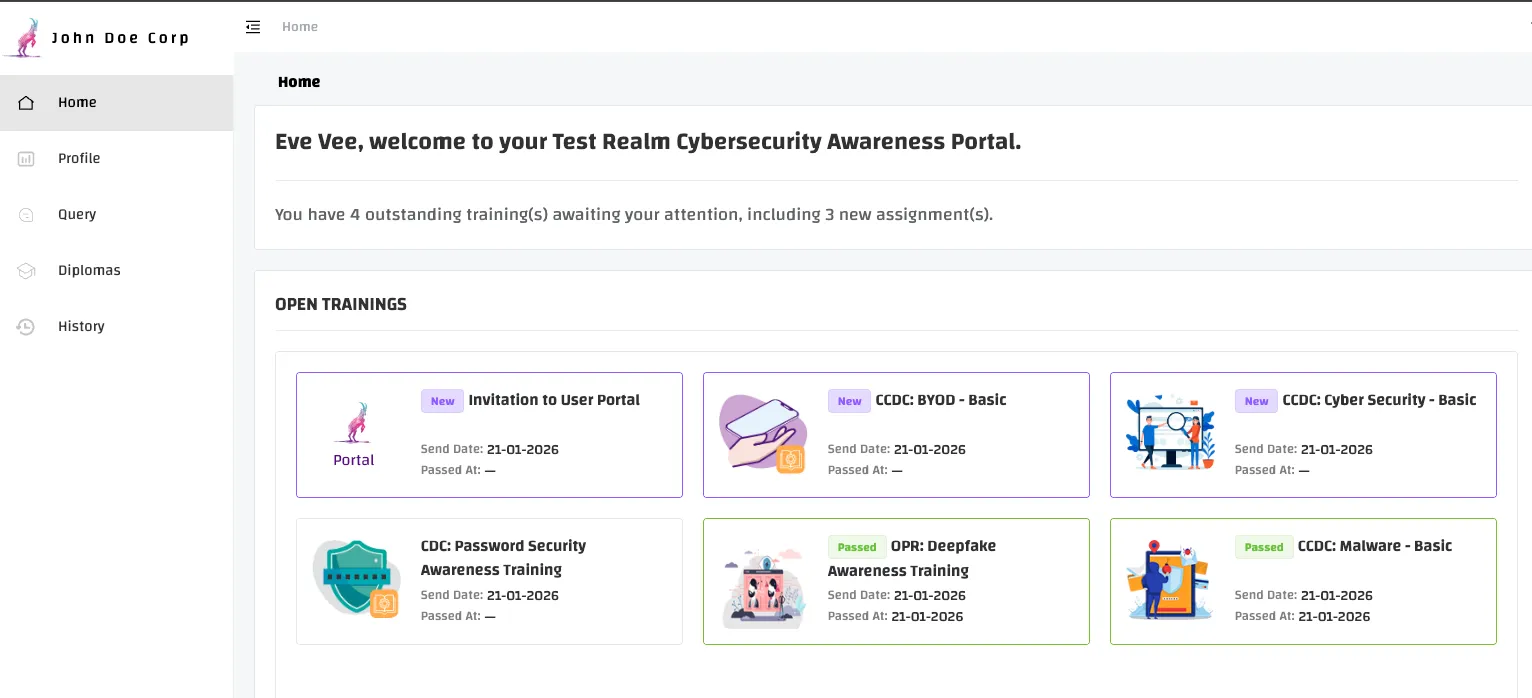
In a nutshell: Our LMS supports SCORM 1.2/2004, HTML, video, and PDF content with full tracking (completion, pass/fail, time) and reporting, including export or API. It also offers automated assignments with dynamic groups and reminders, multi-level multi-tenancy, MFA, and SSO, including LDAP or Azure AD sync.
Multi AD on realm level: the beauty of a smart application architecture
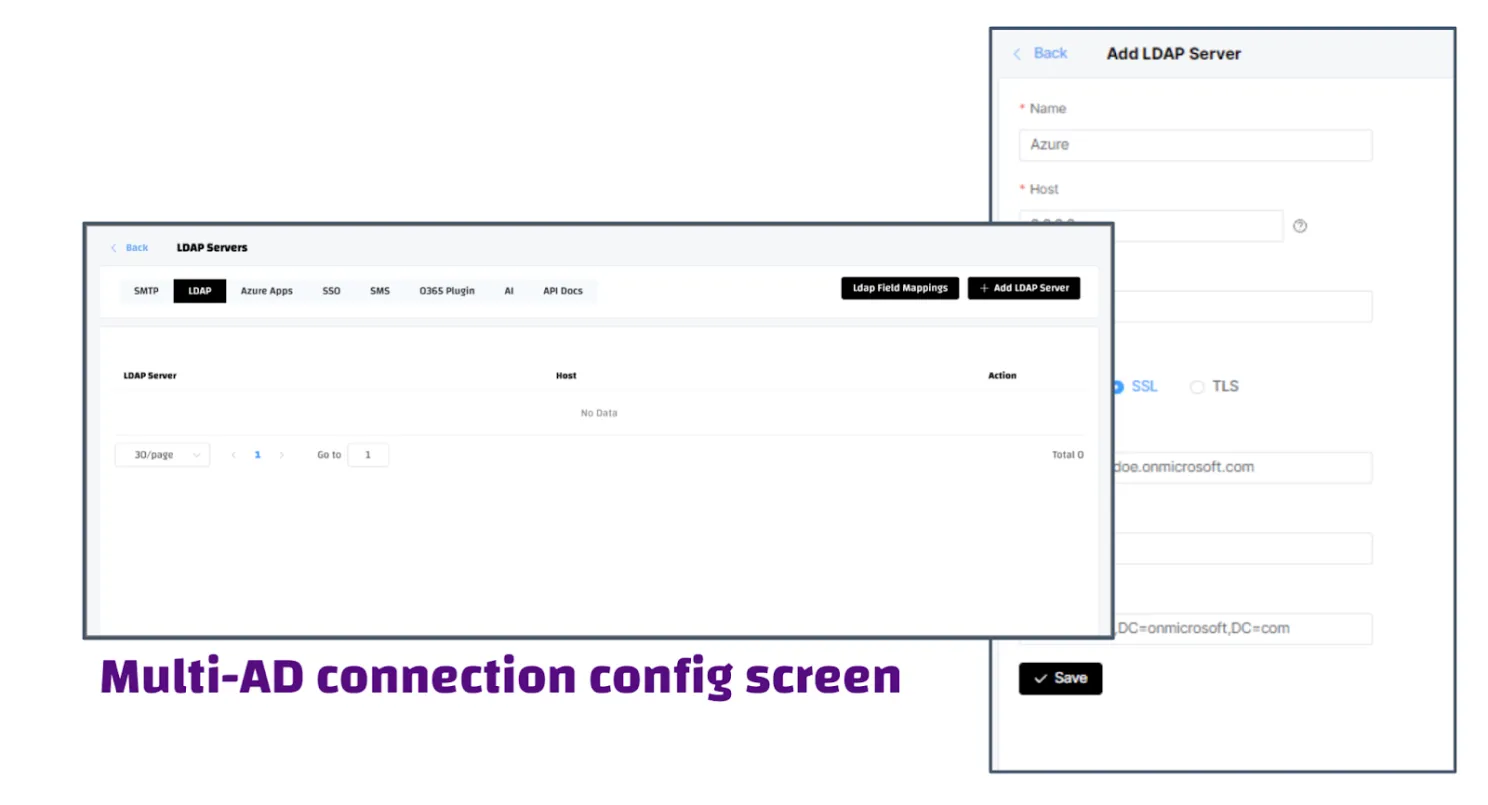
From a client management perspective, a CYBERDISE instance has three levels: instance level, client level, and realm level. This allows the John Doe Corp group of companies to be created as an independent and segregated client, with a separate realm for each subsidiary. A new feature is that an unlimited number of Active Directories or LDAP connections can now be added at the realm level. This means that employees spread across multiple ADs can be served with awareness activities in the same realm (sub-client) – flexibility for everyone! 🙂
Two nerdy but cool features: HLS streaming and button languages
Last but not least, here are two small tech features that I really like. The LMS and video player now support HLS streaming, so you no longer have any problems with videos in training modules, even on iPhones and iPads.
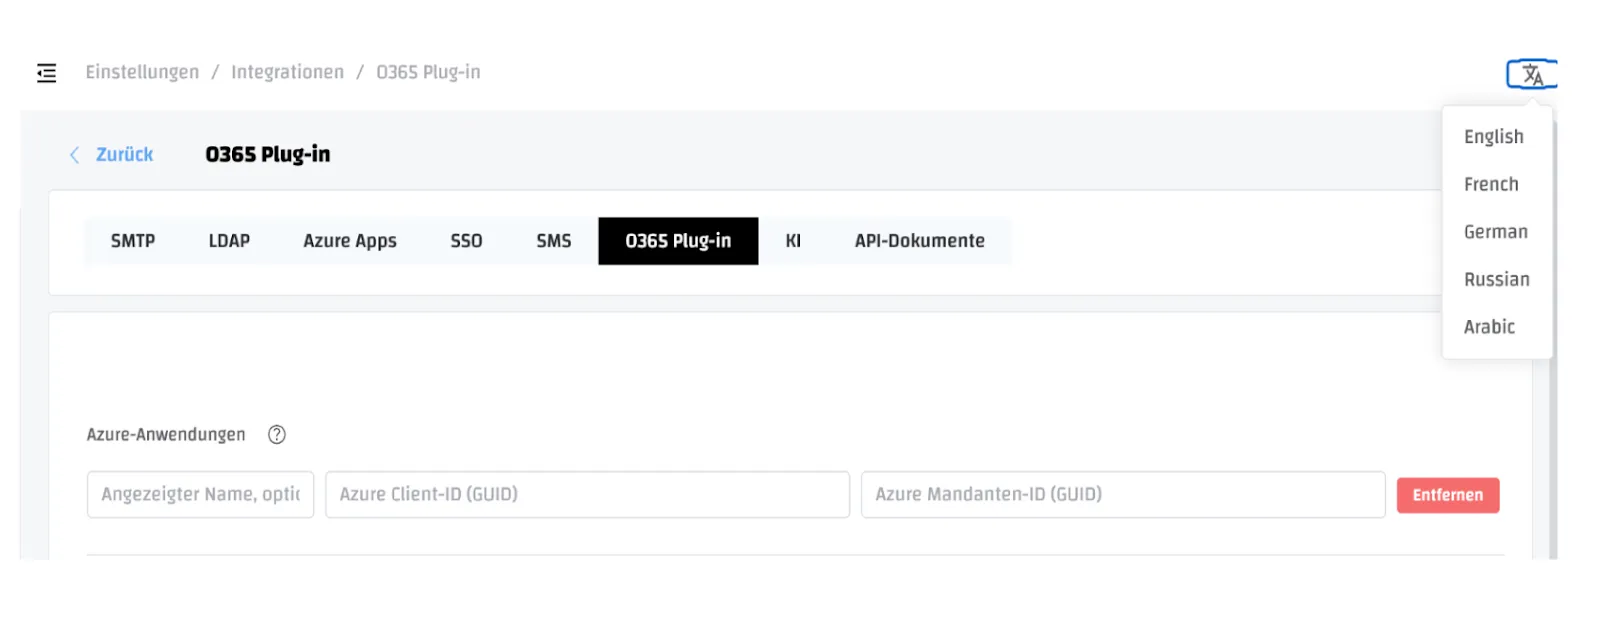
And the button can now be configured even more precisely, and the phishing incident plugin (Phish Button) is now available in 16 standard languages!
Best regards, Palo