Skip to content

Blog

Research, guides and category thinking on Behavioral Defense.

social-engineeringClickFix: when the user runs the attack

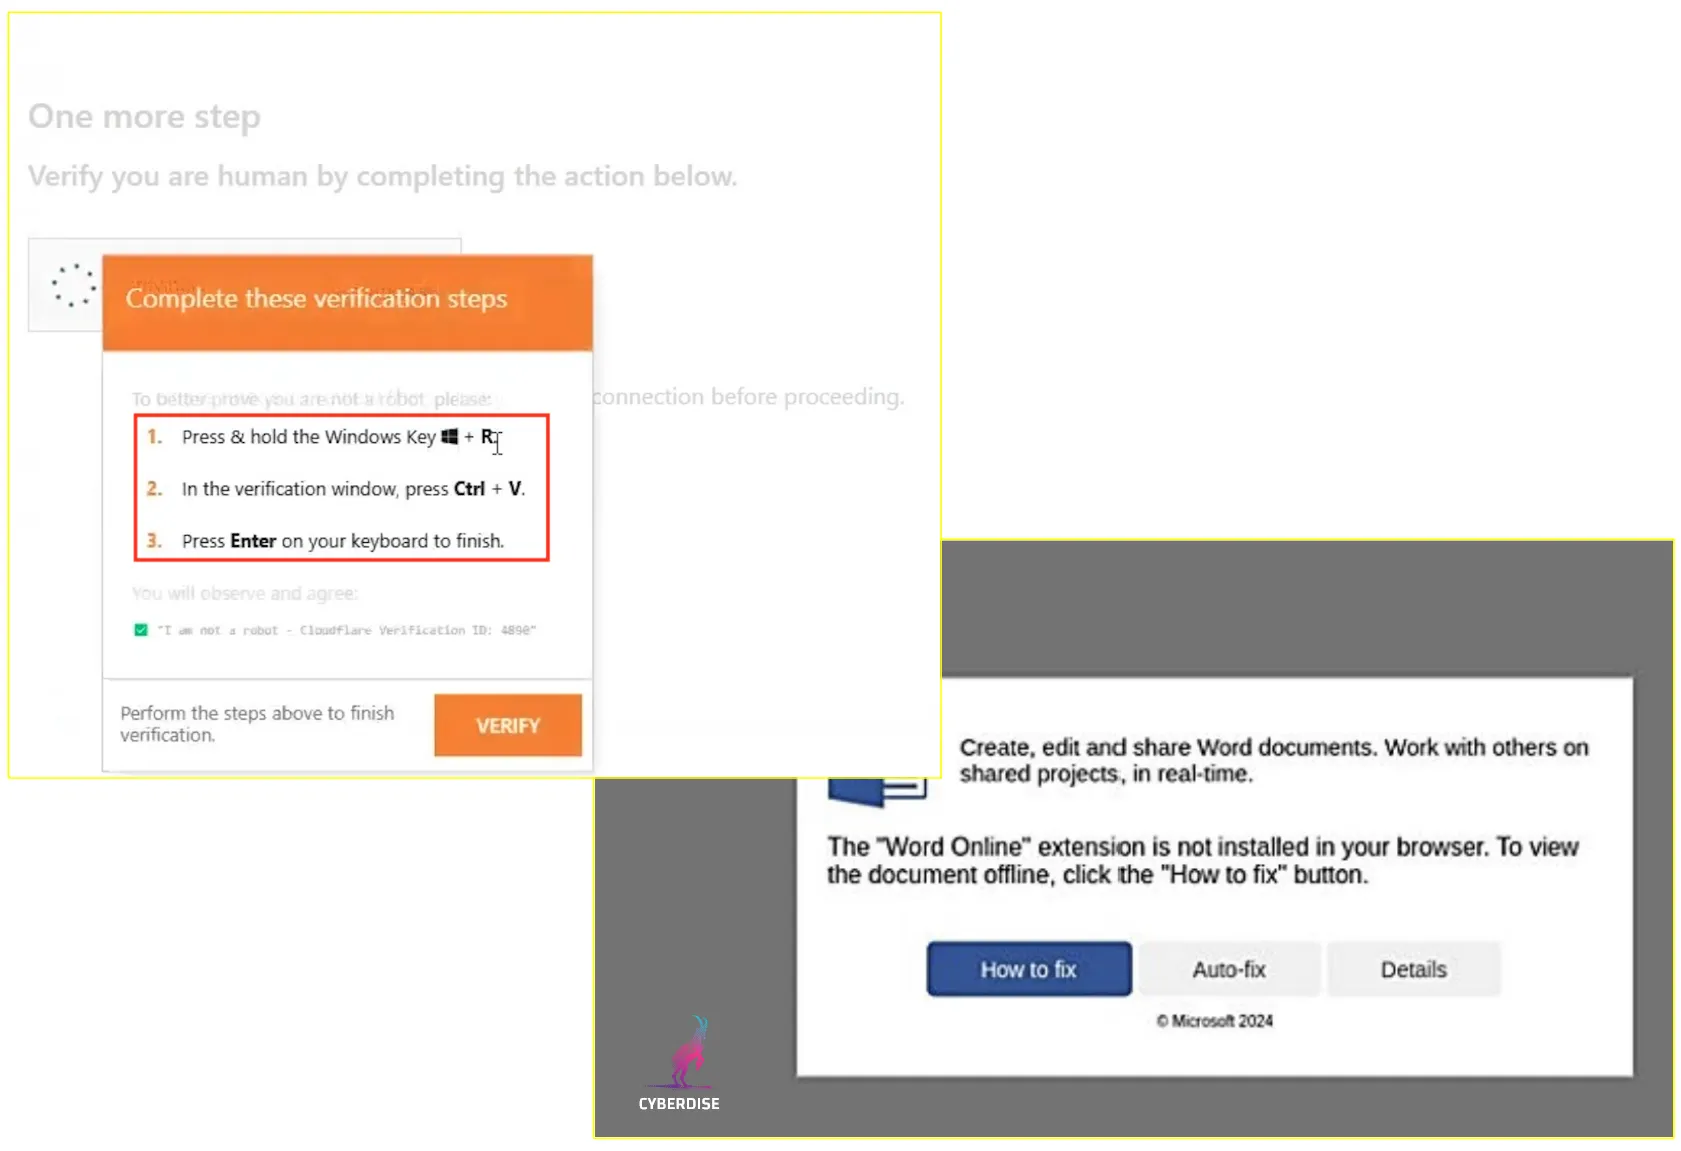
ClickFix does not ask employees to open a malicious attachment. It guides them through what looks like a routine repair or verification step until they execute the attack themselves. Here is how to build a ClickFix simulation in Cyberdise Awareness — from scenario selection to delivery and measurement.
threat-landscapeThe Zeitenwende of Attack Vectors

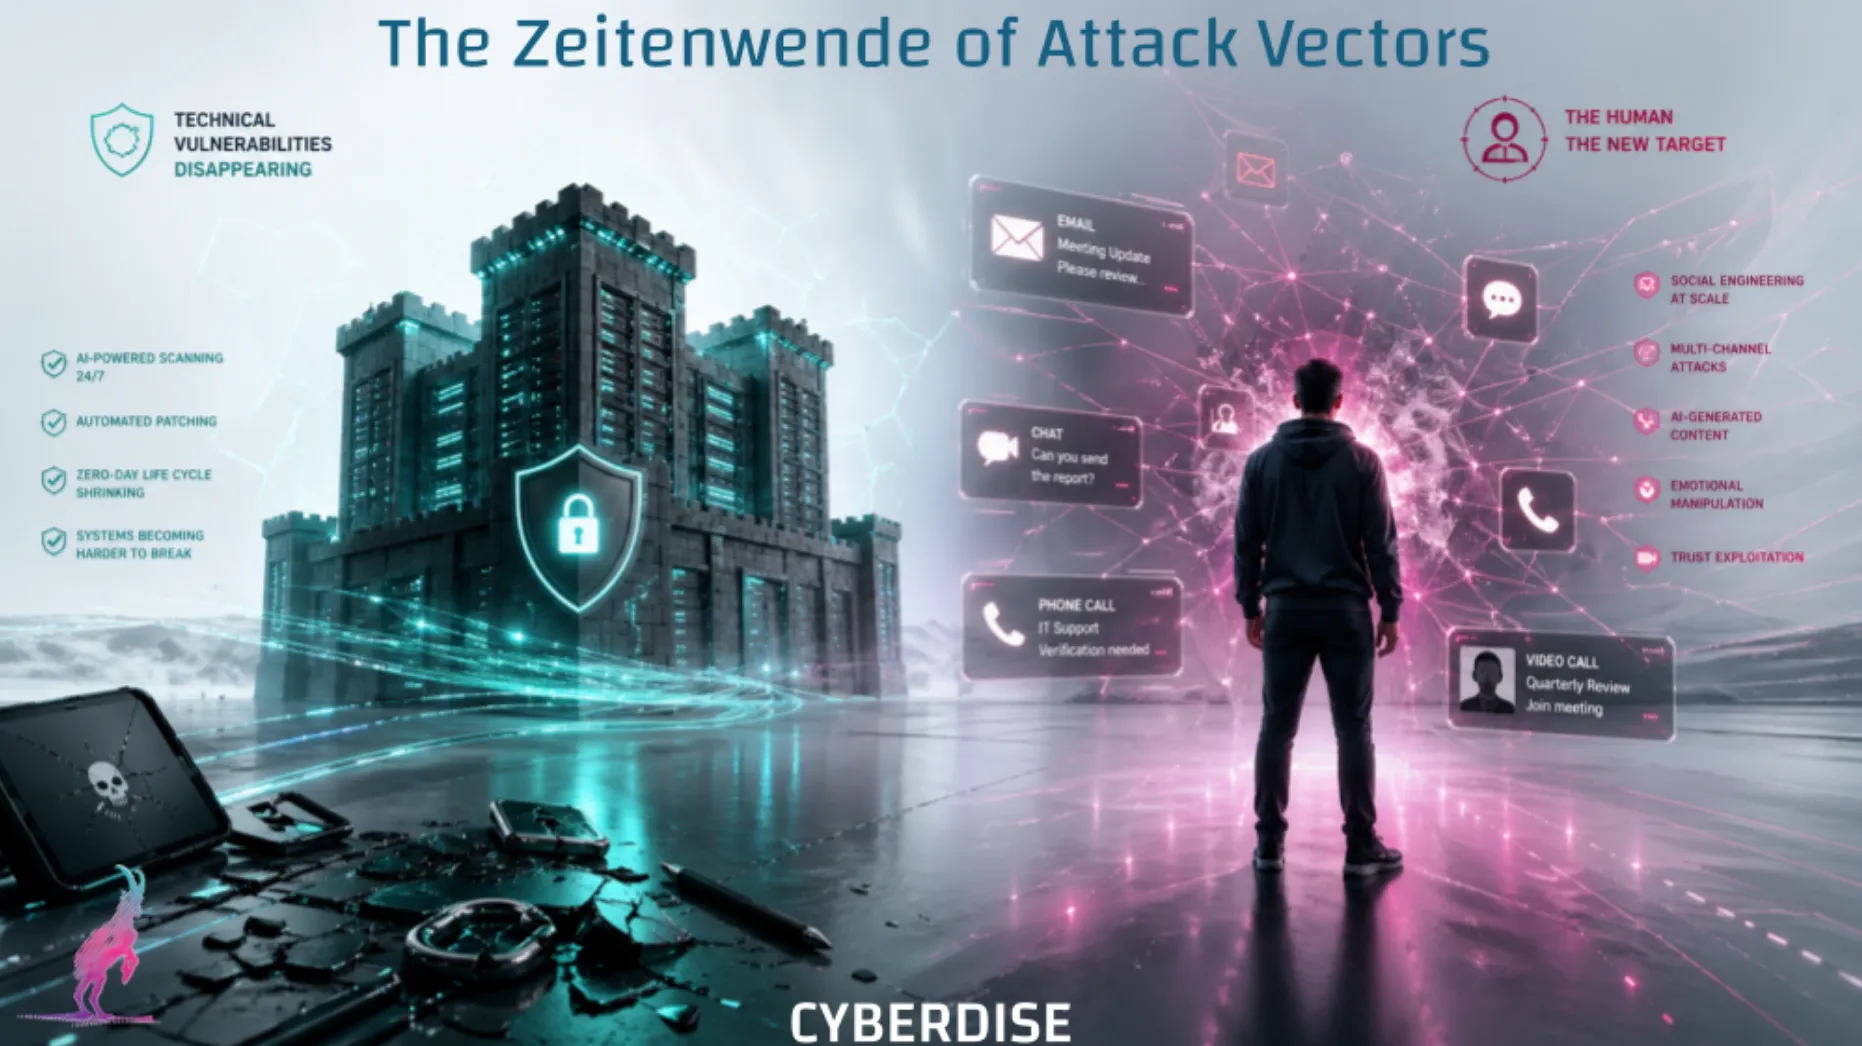
What happens when technical vulnerabilities disappear in the future – and humans become the primary target? There is a lot of talk right now about AI becoming the better hacker. That is only the first phase; the real shift begins after it.

pressBehavioral Defense Engineering: Cyberdise in itbusiness.ch

Swiss IT publication itbusiness.ch has featured Cyberdise, and the headline says it all: cyber defense begins with behavior. Its June 2026 article argues that security awareness training alone no longer protects organizations.

bdeAwareness doesn't stop attacks. Behavior does.

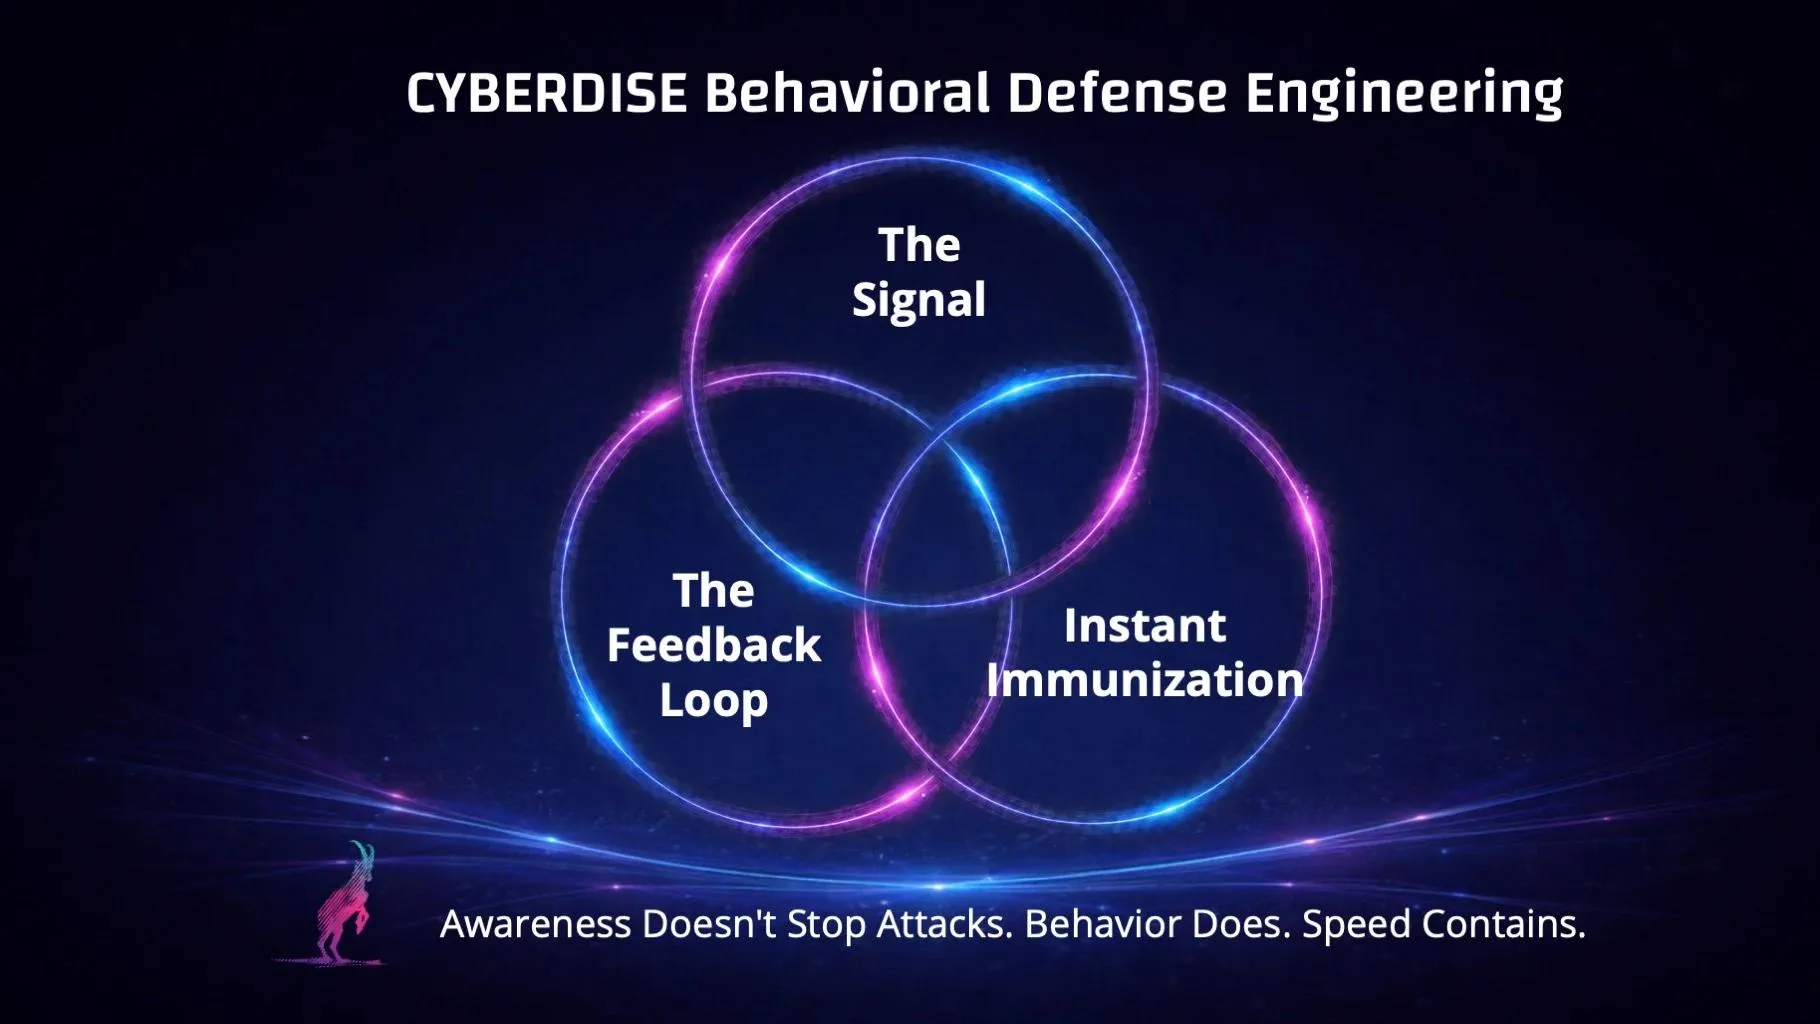
For two decades, security awareness programs have transferred theoretical knowledge — and measurable organizational risk stayed high. With Behavioral Defense Engineering and platform version V3.2, CYBERDISE treats human behavior as an operational part of IT security instead of a compliance checkbox.

bdeThe Next Giant Leap: Why It Is Time to Redefine Human Cybersecurity

Cyberdise is moving from traditional security awareness to Behavioral Defense Engineering (BDE). Employees already know phishing is dangerous, yet under the pressure of daily business they still click: the issue is not a lack of knowledge, it is a behavioral gap.

comparisonDefender Attack Simulator: strengths and limits

Microsoft Defender for Office 365 ships with its own phishing simulation and awareness platform. In some areas it is very good. In others, structural limits appear very quickly. This is a deliberately balanced look at both sides.

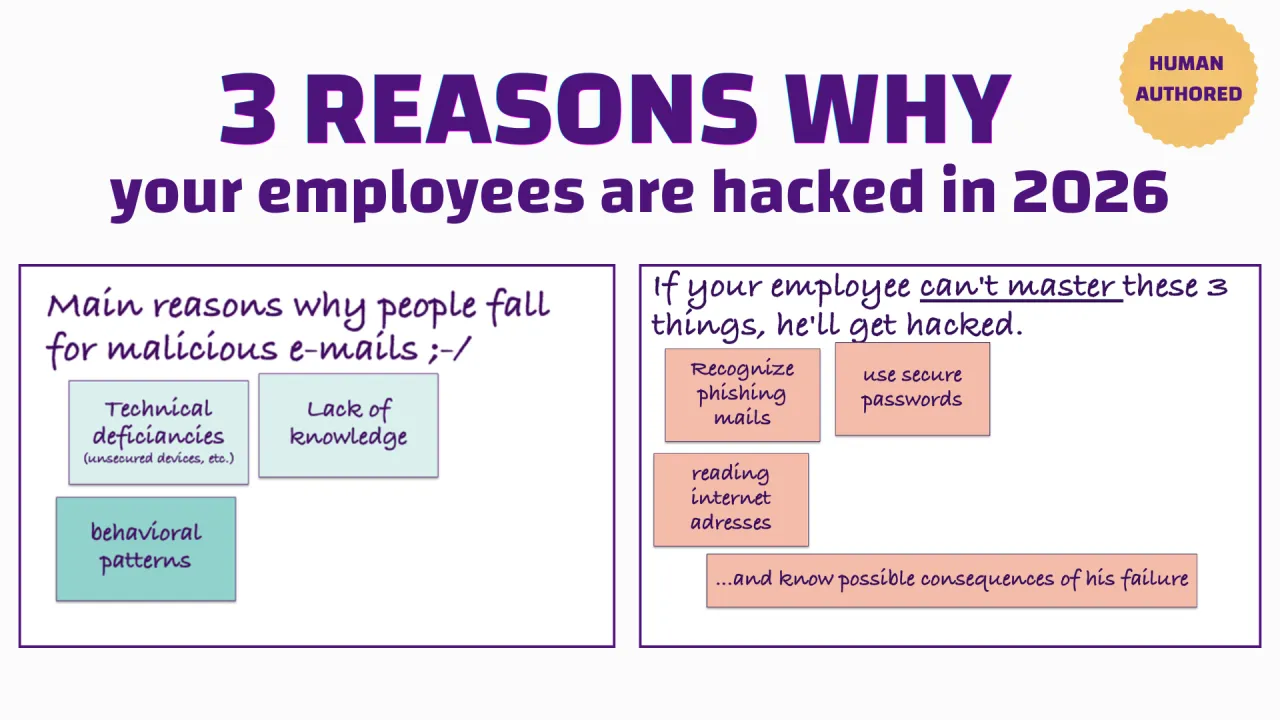
human-riskThe Three Reasons Why Employees Get Hacked

Nearly half of all successful cyberattacks start with a negligent employee. Search engines will tell you it comes down to phishing, weak passwords and careless data handling. Look closer and all three say the same thing: this is about people.

awarenessNIS2 Is in the Budget - Not Yet in the Systems

A study by CIO / CSO / Computerwoche, based on 324 interviews with senior IT decision-makers across DACH, shows how NIS2 is reshaping the way organisations think about cybersecurity. But compliance and actual resilience are still far apart.